Cloud Event Processing, Agent Orchestration &
Cryptographic Microservice Infrastructure
Architecting distributed event-driven microservices (hpy-eventx), autonomous multi-agent orchestration systems (agent-orchestrator), high-performance edge attribution (agent-attr), and zero-knowledge cryptographic authentication.
Cloud Microservices & Distributed DAGs
High-reliability serverless event processing and analytics pipelines handling mission-critical health telemetry.
Distributed state consistency, topological DAG execution order, and cold-start latency mitigation.
Zero-duplicate event processing, AWS Step Functions DLQ automation, and real-time DuckDB/Athena analytical reporting.
Cloud Microservices & Agent Architecture
Select any cloud project below to view its details.
Cloud Event Exchange (`hpy-eventx`)
Distributed event-driven DAG workflow engine with multi-source lazy model rehydration, JSON-Logic predicates, Step Functions retries, and timestamp-preserving S3 DLQ inbox.
Autonomous Agent Orchestrator (`agent-orchestrator`)
Multi-agent autonomous platform featuring bidirectional Jira/GitHub webhook synchronization, hierarchical ticket graph seeding, collaborative agent personas, and multi-server RPC dispatch.
Partner Webhooks & Data Attribution (`agent-attr`)
Serverless edge routing and data attribution platform built on CloudFront Lambda@Edge, sub-domain anti-stripping engine, 90-day HTTP-only cookies, and an in-house Branch.io replacement.
Backend Cryptographic Auth (`backend-crypto-auth`)
Decentralized cryptographic authentication enabling anonymous clinical trial enrollment for CROs, on-device derived key encryption, and zero-knowledge patient data protection.
Cloud Event Exchange (hpy-eventx)
High-throughput distributed workflow engine processing asynchronous event streams, topological DAG logic gating, forward/inverse state delta calculations, and downstream marketing/analytics telemetry.
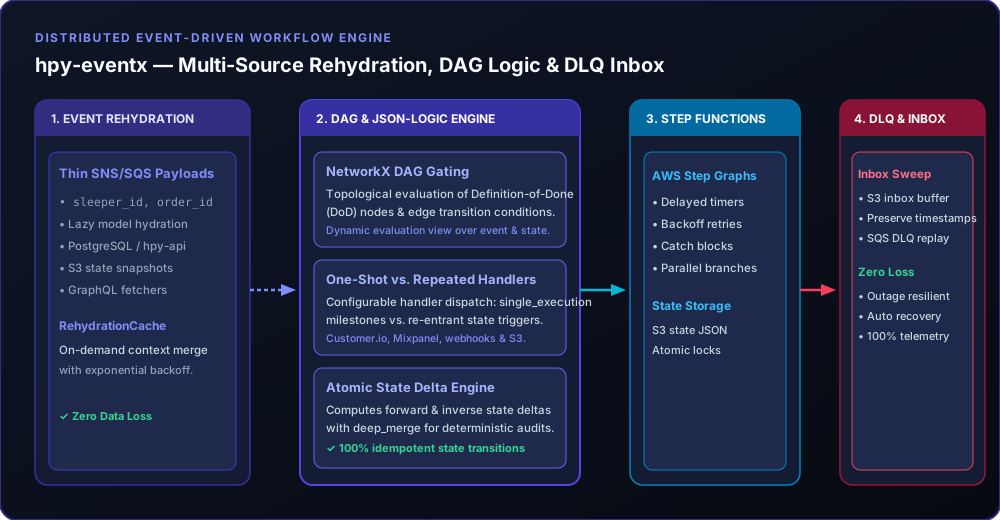
Multi-Source Rehydration, DAG Traversal & DLQ Inbox Engine
Executing deterministic state transitions and fault-tolerant event routing across heterogeneous cloud backends.
- ✓Multi-Source Lazy Model Rehydration: Compact SNS/SQS event payloads carry thin primary key references (e.g.,
sleeper_id,order_id). Built on-demand rehydration caching (RehydrationCache) resolving full entity models across PostgreSQL (hpy-api), S3 state snapshots, GraphQL, and REST backends with exponential backoff retries. - ✓Logic-Evaluation Gating & DAG Traversal: Implemented NetworkX Directed Acyclic Graph (DAG) traversal in topological order, evaluating Definition-of-Done (DoD) nodes and conditional edge predicates using
json-logicagainst dynamic evaluation views ofeventandstate. - ✓Configurable Handlers & Execution Modes: Engineered modular event handlers (Customer.io, Mixpanel, S3 telemetry, webhooks) with support for
single_execution(one-shot milestone completions) vs. repeated/re-entrant triggers upon state mutations. - ✓AWS Step Functions Retry Orchestration: Integrated AWS Step Functions state machine execution graphs to orchestrate scheduled workflow delays, exponential backoff retries, and atomic distributed state persistence.
- ✓Complex DLQ & Timestamp-Preserving S3 Inbox: Built a dual-layer fault-tolerance system featuring SQS Dead Letter Queues (DLQ) and an S3-backed event inbox buffer that preserves original event timestamps during sweep replays to maintain telemetry fidelity during downstream outages.
- ✓Deterministic State Delta Engine: Computed forward and inverse state deltas with recursive deep-merging, guaranteeing 100% idempotent user state transitions and complete historical auditability.
Autonomous Multi-Agent Orchestrator (agent-orchestrator)
Distributed multi-agent execution platform coordinating autonomous coding, testing, documentation, and backlog management across heterogeneous compute clusters.
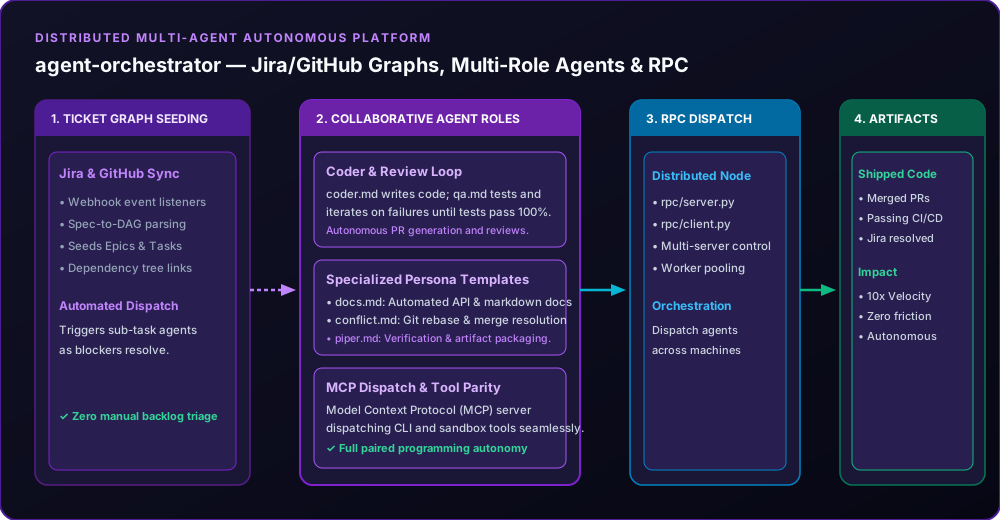
Ticket Graphs, Collaborative Agent Roles & Multi-Server RPC
Orchestrating end-to-end engineering lifecycles from Jira specification decomposition to verified PR mergers.
- ✓Tight Jira & GitHub Bi-Directional Integration: Synchronized with Jira issue webhooks and GitHub PR/commit lifecycle webhooks, enabling agents to automatically transition tickets, post status comments, and open pull requests.
- ✓Hierarchical Ticket Graphs for Jira Seeding: Engineered automated specification parsers that transform technical requirement docs into structured Directed Acyclic Graphs (Epics → Tasks → Sub-tasks with dependency links) to seed Jira backlogs with zero manual triage.
- ✓Collaborative Multi-Role Agent Personas: Designed specialized role templates with iterative review loops:
pm.md(backlog decomposition),coder.md(feature implementation),qa.md(automated test execution),docs.md(technical docs),conflict.md(git merge resolution), andpiper.md(pipeline packaging). - ✓Distributed Multi-Server Agent RPC Control: Architected an RPC client/server engine (
hpyagent/rpc/) allowing a central orchestrator to monitor, dispatch, and control agent tasks across multiple physical servers, cloud nodes, and developer machines. - ✓Model Context Protocol (MCP) Server & Dispatch: Built an internal MCP server with full tool dispatch parity, equipping agents with standardized CLI execution, sandbox file inspection, and diagnostic logging tools.
- ✓Self-Healing Test & Refinement Loops: Automated iterative execution where
qa.mdexecutes test suites, diagnoses failures, and hands execution back tocoder.mduntil 100% of test assertions pass.
Partner Webhooks & Data Attribution (agent-attr)
Serverless edge routing, privacy-preserving attribution engine, and in-house Branch.io replacement managing partner conversion funnels.
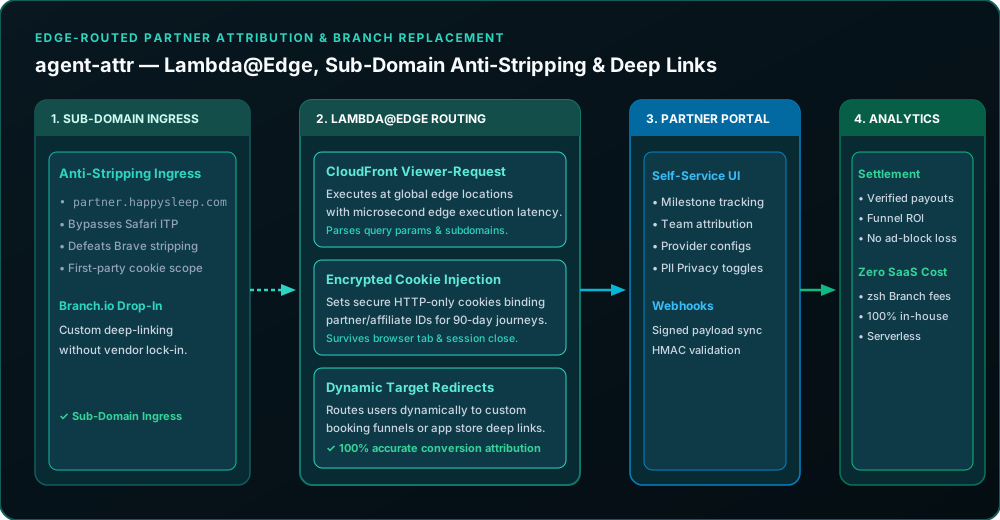
Lambda@Edge, Sub-Domain Anti-Stripping & Deep-Link Routing
Delivering 100% accurate conversion attribution while eliminating third-party SaaS tracking platforms.
- ✓Lambda@Edge High-Performance Routing: Deployed AWS CloudFront Lambda@Edge viewer-request interceptors executing globally with microsecond edge execution latency.
- ✓In-House Branch.io Replacement Platform: Developed custom mobile deep-linking, deferred routing, and web-to-app attribution infrastructure, completely replacing Branch.io and saving significant SaaS licensing costs.
- ✓Sub-Domain Attribution Anti-Stripping Engine: Routed partner traffic through dedicated first-party sub-domains (
partner.happysleep.com), preventing Safari ITP, Brave, and ad-blockers from stripping standard query parameters (utm_*,ref). - ✓First-Party HTTP-Only Cookie Binding: Injected secure, encrypted 90-day attribution cookies surviving browser tab closures and multi-touch patient conversion journeys.
- ✓Comprehensive Partner Portal & UI: Built a self-service management interface for tracking conversion milestones, provider/clinic attribution, commission structures, and team rosters.
- ✓Granular PII Privacy Toggles & Webhooks: Integrated webhook delivery pipelines with configurable HIPAA-compliant PII filtering and HMAC-SHA256 signature verification.
Backend Cryptographic Auth & Zero-Knowledge Vaults
Pure cryptographic authentication microservice enabling anonymous clinical trial enrollment and zero-knowledge patient data encryption.
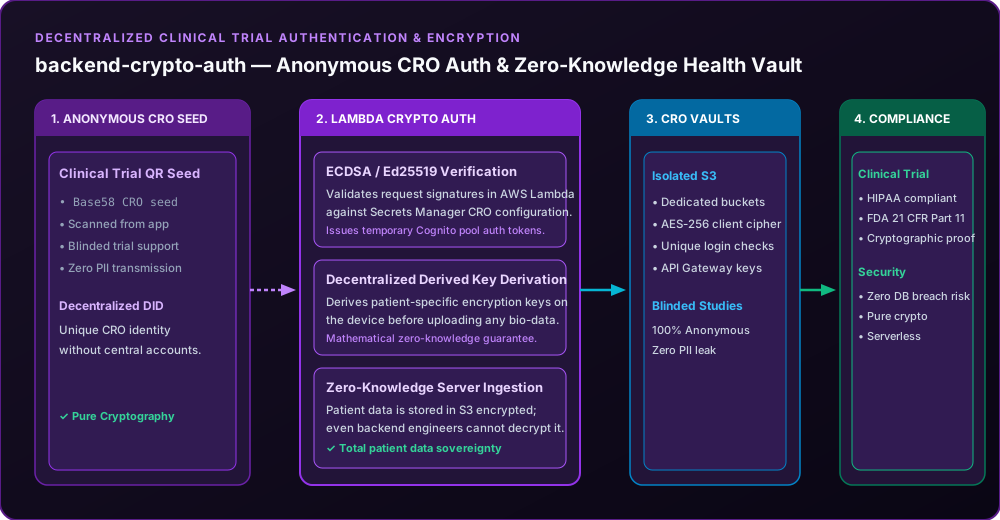
Anonymous CRO Authentication & Decentralized Patient Vaults
Enabling blinded clinical research with mathematical zero-knowledge data sovereignty guarantees.
- ✓Anonymous Authentication for CRO Blinded Trials: Implemented pure cryptographic authentication enabling Clinical Research Organizations (CROs) to conduct double-blind clinical trials where patients authenticate via QR-scanned seeds without transmitting PII.
- ✓Decentralized Zero-Knowledge Patient Encryption: Leveraged on-device derived cryptographic keys to encrypt biometric time-series and sleep data before cloud upload, guaranteeing that even backend platform operators cannot view unencrypted patient health data.
- ✓AWS Lambda Signature Verification: Engineered serverless ECDSA/Ed25519 cryptographic signature verification validating client request tokens against AWS Secrets Manager CRO configurations.
- ✓Automated Cognito Pool & API Gateway Gating: Exchanged verified cryptographic signatures for temporary scoped AWS Cognito auth tokens and throttled API Gateway access keys.
- ✓HIPAA & FDA 21 CFR Part 11 Compliance: Delivered mathematically verifiable data sovereignty and cryptographic audit trails for clinical medical device validation.
- ✓Decentralized Identifier (DID) Architecture: Bound each research institution and trial cohort to unique W3C Decentralized Identifiers, eliminating centralized password databases and single-point-of-breach vulnerabilities.