Platform Security, AOSP Sandboxing
& High-Availability Infrastructure
About Conrad
→
Engineering hardened, de-Googled Android mobile platforms (ClearOS) with elevated SELinux IPC bridges. Expertise with bare-metal Windows Server Failover Clusters and enterprise Root PKI.
AOSP Platform Security & Bare-Metal HA Ops
Building a sovereign de-Googled OS platform for biometric identity alongside high-availability bare-metal infrastructure for hospital operations.
Enforcing strict Enforcing-mode zero-denial SELinux isolation with cross-app URI grants, StrongBox TEE signing, and WSFC failover clusters.
Production-ready custom AOSP manifest, 72+ vendor patches, 5 AIDL services, and 6 continuous years of 99.9% bare-metal uptime.
Enforcing Privacy in Hostile Computing Environments
Modern operating systems often trade user privacy and sovereignty for vendor telemetry lock-in. Building a fully self-sovereign, de-Googled mobile operating system (ClearOS) required solving deep structural challenges in the Android Open Source Project (AOSP): the platform's strict app_domain sandbox prevents background system daemons from backing up encrypted user databases across sandbox boundaries without compromising device security.
Simultaneously, mission-critical healthcare backends and identity directories require zero-downtime database failover and robust physical infrastructure that can survive hard hardware faults without data loss.
Elevated FIFO IPC, SELinux Policies & Bare-Metal WSFC
Bridging Android OS binder isolation with elevated FIFO pipes and architecting multi-node active/passive failover clusters.
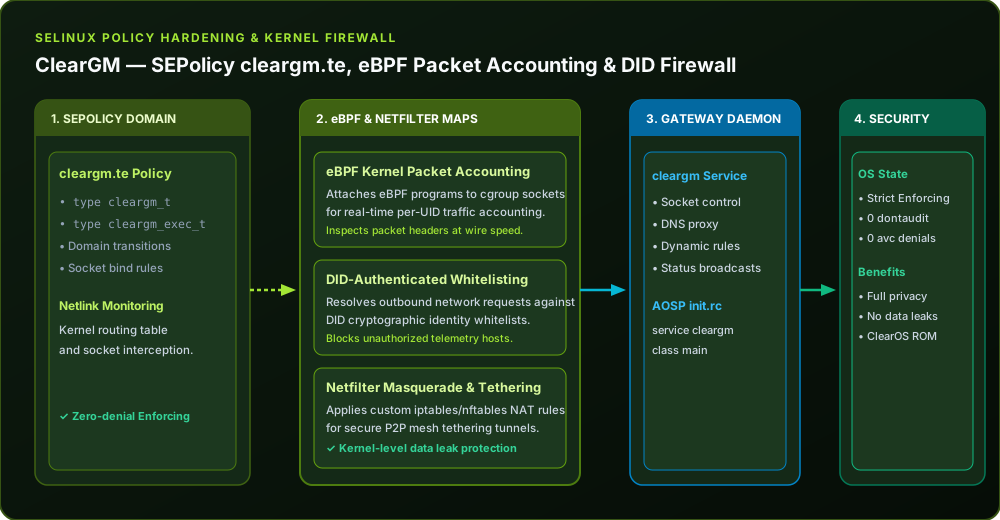
Privileged Gateway Management & Elevated IPC
Bypassing app-domain isolation through elevated UNIX FIFOs and specialized SELinux domain rules.
- ✓72 Single-Handed AOSP Framework Patches: Modified Android's Grants Manager Service and Content URI providers to enable background encrypted state backup across sandboxes without root escalation vulnerabilities.
- ✓Elevated FIFO IPC & SELinux Hardening: Built isolated bidirectional UNIX FIFO pipes managed by privileged native daemons, governed by strict DAC and SELinux type-enforcement rules.
- ✓Bare-Metal Failover Clusters (WSFC): Assembled physical server nodes with dedicated heartbeat Ethernet rings, SAS/iSCSI SAN storage, and automated SQL Server failover.
- ✓Enterprise PKI & Active Directory: Multi-tier Root and Subordinate Certificate Authorities enforcing automated certificate issuance for 200+ domain endpoints and custom Android KeyStore biometrics.
Quantified Outcomes & Security Footprint
Explore the low-level AOSP C++ code, SELinux policy files, and bare-metal cluster specifications: