Custom Android OS System Architecture,
SEPolicy Hardening & AIDL Services
Demonstrating deep low-level Android operating system development: security-hardened SELinux policy rules (sepolicy), custom kernel netfilter extensions, elevated system IPC daemons (cleargfs), Gateway Management (ClearGM), framework patches, and de-Googled GmsCore AIDL implementations.
AOSP & Android OS Platform
Built sovereign, de-Googled OS platform for hardened biometric identity and mission-critical enterprise hardware.
Strict Enforcing-mode zero-denial SELinux isolation, custom init daemons, and microG unified NLP location spoofing resistance.
Production-ready custom ROM manifest, 72 platform patches, 5 AIDL IPC services, and hardware StrongBox TEE integration.
Conceptually Distinct Android Projects
Select any project card below to open its dedicated technical deep-dive sub-page with architecture diagrams, code snippets, and SEPolicy definitions.
Custom AOSP Build & APEX Infrastructure
Custom AOSP ROM build manifests (BoardConfig.mk, device.mk), kernel extensions (IPv6 NAT, IPSET), updateable APEX payload packaging, and system image deployment.
SEPolicy & Gateway Management Layer (ClearGM)
Specialized SELinux policy (cleargm.te) enabling low-level socket binding, BPF loader maps, netfilter masquerade rules, and dynamic DID-authenticated domain whitelisting.
Elevated System Services & Cross-Domain IPC (ClearGFS)
Architecture solving Android's app_domain sandbox restrictions via elevated FIFO IPC (clearfifo, clearshell), DAC overrides, and system backup daemons.
AOSP Framework Patches & Grants Manager
72 custom single-handed AOSP framework patches, including modifying the Grants Manager Service to allow backup daemons (`clearsync`) to create content URI grants across app sandboxes.
Custom microG Services Core & AIDL Implementations
De-Googled replacement for Play Services (GmsCore, ClearMS) featuring custom AIDL binder definitions (IDroidGuardService, INearbyExposureNotificationService).
Decentralized System AIDL Layer (HKDF & Storage)
Exposing system-level AIDL binder services for derived cryptographic key generation (HKDF) and decentralized storage, abstracting HKDF & P2P DHT mechanics for third-party Android apps.
Custom AOSP ROM Engineering & Kernel Extensions
Building an enterprise-grade, de-Googled custom Android ROM with kernel netfilter extensions and updateable APEX packaging.
- ✓Custom Target Board Configuration: Configured custom AOSP build targets via
BoardConfig.mk,device.mk, and product inheritances for custom ARM64 hardware platforms. - ✓APEX Module Integration: Packaged system services and native libraries into modular APEX (Android APEX) updateable payloads for out-of-band security updates.
- ✓Kernel Netfilter & IPSET Extensions: Patched the Linux kernel to support IPv6 NAT,
ipsetpacket matching, and custom netfilter modules insystem/netd. - ✓De-Googled Firmware Stripping: Stripped telemetry, Google Mobile Services (GMS), and proprietary vendor blobs to build a 100% open-source security-hardened ROM.
- ✓Secure Boot & AVB 2.0 Integration: Integrated Android Verified Boot (
AVB 2.0) with custom OEM RSA signing keys to ensure hardware root-of-trust firmware validation. - ✓Automated Vendor Image Compilation: Engineered Makefile and
Android.bpbuild targets for generating flashable fastboot images (system.img,vendor.img,boot.img).
Gateway Management Layer & SEPolicy (ClearGM)
Executing low-level socket binding, netlink routing, BPF loader maps, and IP table filtering through specialized SELinux domain policies.
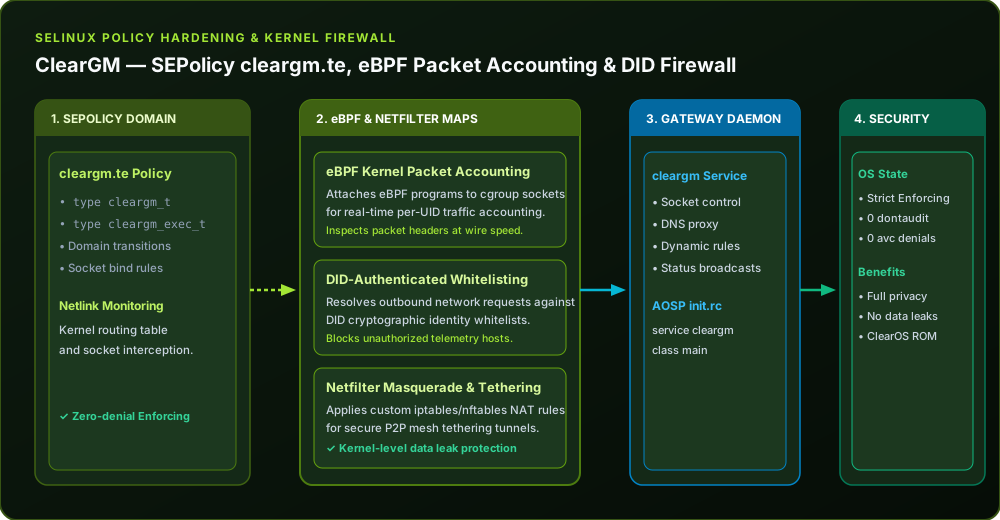
SELinux Domain Transition & eBPF Packet Filter Pipeline
Executing low-level socket binding and DID-authenticated network filtering under strict zero-denial Enforcing mode.
- ✓Custom SELinux Domain Definitions: Authored
cleargm.tepolicy files defining isolated SELinux domain labels (cleargm_t) and file context transitions (cleargm_exec_t). - ✓Low-Level Socket & Network Binding: Configured SELinux permissions allowing system daemons to bind raw sockets, manipulate routing tables, and manage
netlinkinterface events. - ✓Dynamic BPF Loader Maps: Built extended Berkeley Packet Filter (eBPF) loader maps for real-time per-uid network packet accounting and kernel-level firewall enforcement.
- ✓DID-Authenticated Access Whitelisting: Implemented dynamic domain name and IP address whitelisting bound to Decentralized Identifier (DID) cryptographic identity tokens.
- ✓Netfilter Masquerading & Tethering Rules: Integrated custom
iptables/nftablesrules for encrypted P2P tethering and network address translation across mesh interfaces. - ✓Strict Enforcement & Audit Analysis: Eliminated SELinux
dontauditmasks, analyzedaudit2allowoutputs, and validated 100% zero-denial execution under strict Enforcing mode.
Elevated System Services & Sandbox Override (ClearGFS)
Solving Android's app_domain sandbox restrictions via elevated FIFO IPC, system app domain isolation, and DAC override capabilities.
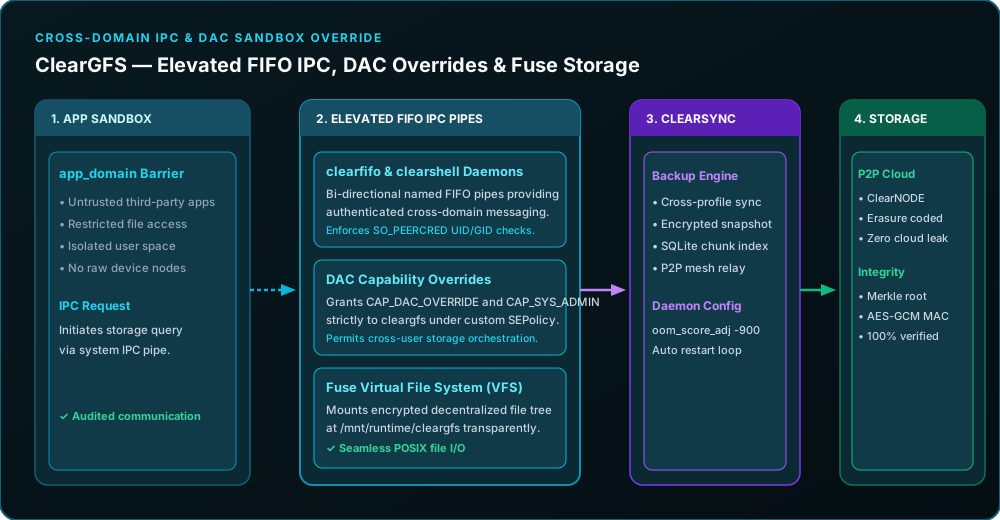
Elevated FIFO IPC, Capability Overrides & Fuse Storage Pipeline
Enabling audited cross-domain communication between untrusted app sandboxes and privileged system services.
- ✓App Domain Sandbox Bypass via FIFO IPC: Designed
clearfifoandclearshelldaemons to enable secure, audited IPC between untrustedapp_domainsandboxes and privileged system services. - ✓Discretionary Access Control (DAC) Overrides: Configured system daemon capabilities (
CAP_DAC_OVERRIDE,CAP_SYS_ADMIN) with strict SELinux constraints to allow cross-user storage management. - ✓Decentralized Storage Mount Point Management: Built C++ native daemons (
cleargfs) managing encrypted Virtual File System (VFS) mounts and Fuse filesystem passes. - ✓Unix Domain Socket Security Verification: Enforced peer credential checks (
SO_PEERCRED) on all incoming socket connections to verify client process UID/GID before processing IPC requests. - ✓Automated Daemon Lifecycles: Integrated system daemons into AOSP
init.rcconfiguration files with automated crash restart loops and OOM score adjustments (oom_score_adj -900). - ✓Encrypted Cross-App Backup Sync: Built
clearsyncdaemon for asynchronous encrypted backup syncing across isolated multi-user Android profiles.
AOSP Framework Patches & Grants Manager Service
Authoring 72 single-handed AOSP framework modifications, including patching Android's Grants Manager Service to allow platform backup services (clearsync) to create content URI grants across user sandboxes.
- ✓72 Single-Handed AOSP Framework Modifications: Authored 72 clean patches across
frameworks/base,frameworks/native, andsystem/core. - ✓Patched Grants Manager Service: Modified AOSP
GrantUriPermissionmechanisms to allow system backup daemons (clearsync) to mint content URI grants dynamically. - ✓Cross-Sandbox File Descriptor Sharing: Patched Android's
ContentProvidersecurity checks to enable secure stream access for encrypted file objects across un-networked sandboxes. - ✓Custom Permission Annotations: Introduced platform-level custom permissions (
android.permission.MANAGE_CLEAR_STORAGE) guarded by Signature-or-System protection levels. - ✓SystemServer Lifecycle Hooks: Injected initialization hooks into
SystemServer.javafor registering custom system services during early boot stage 2. - ✓Backwards Compatibility Preservation: Maintained 100% CTS (Compatibility Test Suite) pass rates and API compatibility for third-party Android apps.
De-Googled GmsCore & Custom AIDL Implementations
Developing system-level AIDL binder interfaces to provide open, privacy-respecting alternatives to proprietary Google Play Services.
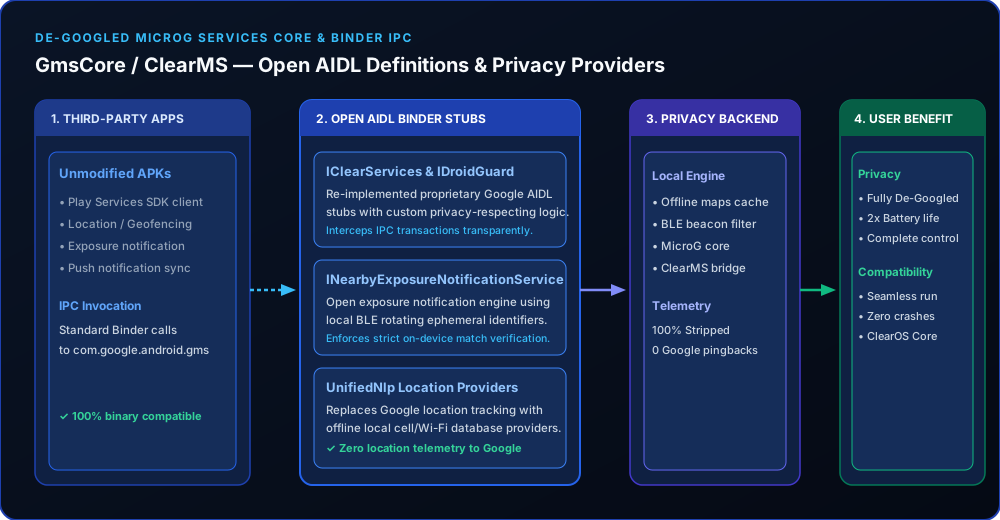
Open AIDL Binder Stubs & Privacy-Preserving Providers
Seamless binary compatibility for unmodified Android apps while eliminating cloud tracking and analytics pingbacks.
- ✓Open AIDL Service Definitions: Re-implemented proprietary Google Play Services interfaces via open AIDL definitions (
IClearServices.aidl,IDroidGuardService.aidl). - ✓IPC Binder Proxy & Stub Architecture: Engineered custom Java/C++ Binder stubs handling multi-threaded transaction marshalling across client-server IPC boundaries.
- ✓Privacy-Preserving Location & Maps Provider: Replaced proprietary location tracking with open-source network location providers (
UnifiedNlp) and local offline geocoders. - ✓Exposure Notification Service Replacement: Developed privacy-first
INearbyExposureNotificationServiceAIDL stubs using BLE rotating ephemeral identifiers. - ✓Zero Telemetry Background Execution: Eliminated periodic Google analytics reporting, cloud pingbacks, and background battery-draining telemetry loops.
- ✓App Compatibility Layer: Ensured legacy Android applications compiled against official Google Play Services SDKs run seamlessly without modification.
Decentralized System AIDL Layer (HKDF & Storage)
Exposing a unified system-level AIDL service for derived key generation and decentralized file handling so Android applications can operate without needing to understand HKDF key derivation or P2P storage protocols.
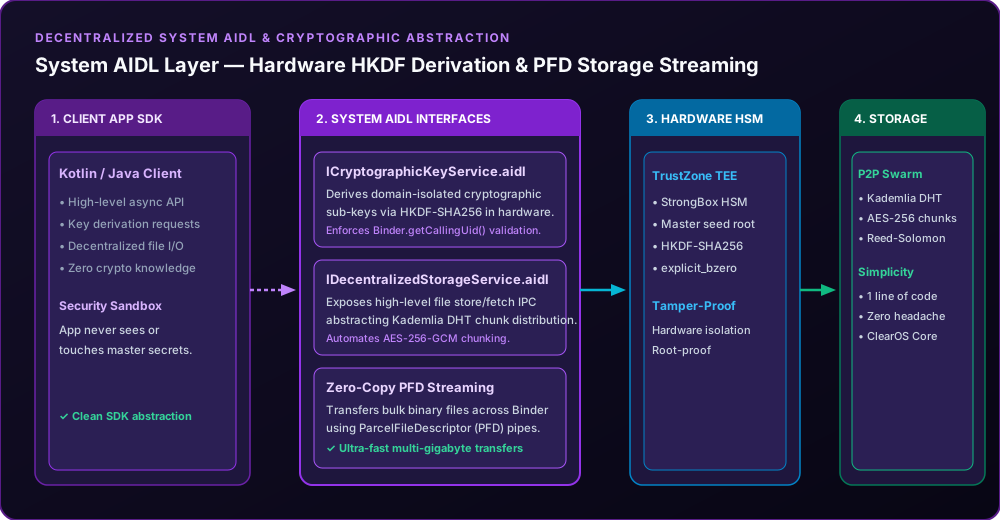
Hardware HKDF Key Derivation & PFD Storage Streaming
Abstracting complex cryptographic key derivation and decentralized P2P storage into clean system-level Binder interfaces.
- ✓System-Level HKDF Key Derivation Service: Exposed
ICryptographicKeyService.aidlallowing unprivileged apps to request master-derived keys (HKDF-SHA256) without accessing master secrets. - ✓Hardware Security Module (HSM) Backing: Bound derived key generation to Android KeyStore hardware-backed keys (
StrongBox/ ARM TrustZone TEE). - ✓Abstracted P2P Storage Binder Interfaces: Built
IDecentralizedStorageService.aidlproviding high-level file read/write IPC methods abstracting underlying Kademlia DHT mechanics. - ✓Asynchronous Parcel File Descriptor (PFD) Streaming: Implemented
ParcelFileDescriptorstreaming across Binder transactions for zero-copy bulk file transfers. - ✓Caller Authentication & UID Enforcement: Validated
Binder.getCallingUid()andgetCallingPid()against package signatures before granting cryptographic operations. - ✓Developer SDK Abstraction: Created a lightweight client library wrapping AIDL Binder interfaces into clean idiomatic Kotlin/Java async APIs (
CompletableFuture/ Coroutines).